Abdulrahman
Al-Gharbi
Full Stack Developer, Android and backend developer, networks and systems, cybersecurity and DFIR.
Full Stack Developer focused on designing and building secure web and Android applications, with hands-on experience in backend systems and open-source digital forensics tools.
- Full Stack Developer
- Web & Android Developer
- Backend & Systems
- Networks & IT
- Security / DFIR
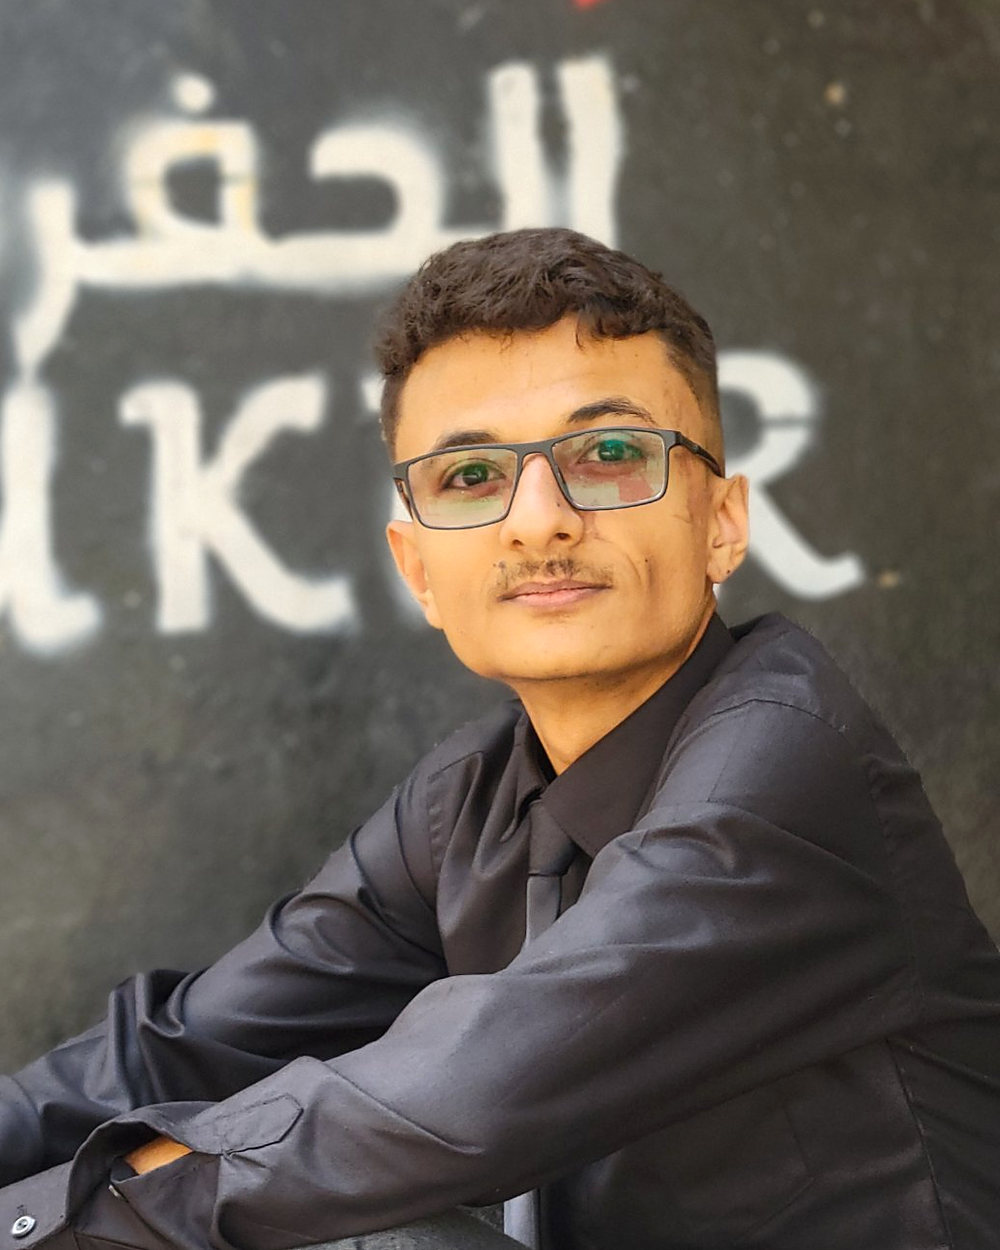
Engineer. Builder. Investigator.
I'm a Full Stack Developer and B.Sc. Cybersecurity & Networks student at Alqalam University (Ibb, Yemen), graduating in 2027 who builds complete systems: web platforms, Android apps, backends and the security tooling around them. My two full-stack products — Nashiit, a multi-tenant Arabic SaaS I built solo, and HatKart, an Android + FastAPI licensing platform — cover everything from database design to secure client apps.
On the security side I write open-source DFIR tools and test them against real-world data instead of relying only on hand-made fixtures. Each one has a validation page that states what was checked, against what, and what was not. I also contribute upstream: 5 merged pull requests to ForensicArtifacts and Velociraptor's registry_hunter, and an open Sigma rule.
Bilingual in Arabic and English, comfortable with Linux, networking fundamentals and CI/CD, and currently expanding into Cloud and DevSecOps. I'm looking for a team where I can build and secure real systems — web and app development, backend and systems engineering, networks and IT, or junior security work — full-time, internship or freelance.
Areas of Work
Full Stack Web Development
Full-stack web apps with Next.js, TypeScript, Node.js and PostgreSQL: multi-tenant architecture, role-based access, dashboards and Arabic RTL interfaces. Nashiit has six user roles, JWT with a blacklist and rate limiting.
Android Apps
Android apps in Kotlin backed by Python/FastAPI APIs, with encrypted local storage (SQLCipher), Android Keystore keys and certificate pinning. HatKart is a licence-management platform for markets without payment gateways.
Backend & Systems
REST APIs, databases and automation in Python and TypeScript, packaged with Docker and tested in GitHub Actions CI. My four open-source tools ship with more than 300 automated tests and documented validation.
Networks & IT Infrastructure
Networking fundamentals from my B.Sc. in Cybersecurity & Networks, plus Linux, traffic analysis with Wireshark, scanning with Nmap and Cisco Networking Academy coursework.
Cybersecurity
Penetration-testing fundamentals (Burp Suite, Metasploit, Nmap) on web, Android and network targets, and secure development in practice: AES-GCM, certificate pinning, JWT hardening, input validation and RBAC.
Forensics & Open Source
Digital-forensics and incident-response tooling (EVTX, NTFS $MFT, disk imaging), plus 5 merged pull requests to ForensicArtifacts (used by Plaso and Timesketch) and Velociraptor's registry_hunter.
Software Projects
Nashiit — نشيط
Multi-tenant Arabic (RTL) SaaS platform for school activity management, built solo. The screenshots below show the running application.
- Six roles with role-based access: Super Admin, School Admin, Supervisor, Guidance Admin, Teacher, Student.
- Workflows: activity creation, supervisor approval queue, saved reports and student notifications.
- Platform admin: school registration, subscriptions and school-year management per tenant.
- Security: JWT blacklist, rate limiting and magic-byte file validation.
HatKart — هات كرت
Full-stack software-licence management for markets without payment gateways: an Android (Kotlin) client and a Python FastAPI backend.
- Client: Kotlin Android app with encrypted local storage (AES-GCM + SQLCipher) and hardware-backed keys in the Android Keystore.
- Backend: FastAPI + PostgreSQL service using HMAC-SHA256.
- Hardening: certificate pinning (MITM prevention), multi-factor device fingerprinting and APK signature verification.
Security Projects
Every project below has a docs/VALIDATION.md listing what was tested on real data, what was tested only with synthetic inputs, and what was not tested. Terminal blocks are excerpts of real runs.
forensic-evidence-toolkit
Forensic imaging with streaming hashes and a chain-of-custody record, an NTFS $MFT parser (attribute lists, extension records, timestomp heuristics) and a Volatility 3 triage wrapper. The $MFT output had 0 differences against an independent parser (dfir_ntfs) on 25,408 real records, and 12,171 reconstructed file paths were identical to The Sleuth Kit's fls. Imaging a real block device produced the same SHA-256 as sha256sum.
Not yet verified: memory triage was checked against the Volatility 3 source code only, not run on a real memory image; the timestomp heuristics flag many legitimately installed files, so they are leads, not proof.
Image: ev.img (3,000,000 bytes)
SHA256 940519577bd29ed5...ffade2b5e48
Verified: YES
$ fet mft samples/MFT --format csv -o out.csv
summary: records=13064, in_use=11837, deleted=1227, directories=981, with_ads=10
win-ir-triage
Parses EVTX logs, evaluates 10 Sigma-subset rules mapped to MITRE ATT&CK, and writes a bilingual (EN/AR) HTML timeline plus JSON and ATT&CK Navigator exports. Run over all 278 files of the public EVTX-ATTACK-SAMPLES dataset: 0 parse errors, 37,364 events, event counts identical to the dataset's own index, and 16 of 16 hand-labelled expectations passing (the labels were chosen after seeing results, so this is not a blind test).
Not yet verified: the false-positive rate (the dataset contains attacks only) and detection of attacks the rules were not written for.
win-ir-triage 0.2.0 - demo
Parsed 1 events from 1 file(s) using 10 rules
2019-05-12 12:52:43Z [medium] IEWIN7 Suspicious Service Installation
(Possible PsExec-style Lateral Movement)
MITRE ATT&CK techniques: T1569.002
smart-audit
Static analyser for Solidity with 18 SWC-mapped rules; five of them read the structure of each function (reentrancy, unchecked calls, unprotected selfdestruct, missing zero-address check, missing event) instead of matching text. HTML, JSON and Markdown reports with a per-contract score, and exit codes for CI. Pattern-based and noisy by design: a first pass, not a replacement for a manual audit.
Not yet verified: behaviour on large real-world contract codebases; it performs no data-flow or cross-contract analysis.
AUDIT SUMMARY 14 finding(s) in 1 contract(s)
[CRITICAL] Reentrancy Vulnerability (line 22)
[CRITICAL] Unprotected selfdestruct (line 35)
[HIGH] tx.origin Used for Authentication (line 29)
VulnerableVault.sol [14 finding(s) · Risk 8.2/10]
BlockSec Auditor
Read-only auditor for Ethereum/EVM nodes: RPC exposure, admin and wallet APIs, CORS, TLS, client version against a curated advisory list, and Geth/Nethermind configuration files. Every outcome is PASS, FAIL, ERROR or SKIPPED; an unreachable node is never reported as clean. The advisory list matched Geth's own advisory data on 241 real releases, and the config audit ran on 91 real Nethermind configs without errors.
Not yet verified: no live node has been scanned yet; the RPC checks are covered by tests against a mock server only. Only Geth has verified advisory data.
FAIL [LOW ] BSA-CFG-001 Configuration File Weaknesses
JSON-RPC exposes dangerous module(s) Admin, Debug, Personal (loopback only)
0 passed, 1 failed, 0 error, 0 skipped (failed: 1 LOW)
- Velociraptor registry_hunter #37Added WDigest (UseLogonCredential) ruleMERGED
- ForensicArtifacts #682Added PuTTY registry key definitionsMERGED
- Velociraptor registry_hunter #35Added LSA Protection (RunAsPPL) ruleMERGED
- ForensicArtifacts #679Added WindowsEventTranscriptDatabaseFile definitionMERGED
- ForensicArtifacts #678Added AnyDesk and TeamViewer definitionsMERGED
- SigmaHQ/sigma #6458New rule: MSBuild Exec Task Temporary Batch File Executed Via CmdOPEN
Skills & Technologies
Courses & Certificates
Ethical Hacker
Cisco Networking Academy
Junior Penetration Tester
NetRiders Academy
Reverse Engineering Android Apps
Online course
Dynamic Instrumentation
Online course
Introduction to Cybersecurity
Cisco Networking Academy
Algorithms & Problem Solving
ProgrammingAdvices
Education
Get In Touch
Open to full-time roles, freelance or hourly projects, and internships in web and app development, backend and systems engineering, networks and IT, and security (DFIR, pentesting fundamentals). Also open to research programs and academic scholarships.